网络、代理与加速合集
命令行代理、GitHub 加速、防火墙与 SSH 配置,以及两种把内核网络栈调快的做法(BBR)。
PowerShell 配置命令行代理
我们将通过创建 PowerShell 函数来实现快速开启和关闭代理的功能。
步骤 1:找到并编辑 PowerShell 配置文件
首先,我们需要找到 PowerShell 的配置文件。如果你还没有创建过,可以用以下命令创建:
1 | if (!(Test-Path -Path $PROFILE)) { |
这会打开你的 PowerShell 配置文件。配置文件的默认路径通常是: C:\Users\你的用户名\Documents\WindowsPowerShell\Microsoft.PowerShell_profile.ps1
步骤 2:添加代理函数
在打开的配置文件中,添加以下函数:
1 | function proxy { |
步骤 3:保存并重新加载配置
保存文件,然后重新启动 PowerShell 或运行 . $PROFILE 来重新加载配置文件。
如何使用
现在,你可以在 PowerShell 中使用以下命令:
- 输入
proxy来启用代理 - 输入
unproxy来禁用代理 - 输入
check-proxy来查看当前的代理设置
注意事项
- 这个设置只影响当前的 PowerShell 会话,不会影响其他应用程序或系统级的代理设置。
- 如果你的代理地址和端口不是
127.0.0.1:7890,请相应地修改函数中的 URL。 - 如果你的代理需要认证,你需要修改函数来包含用户名和密码。
bash/zsh:
1 | proxy |
cURL 查询公网出口 IP
几个网址
- ip-api.com(推荐,速度快)
- ipecho.net(推荐)
- 百度(效果也不错)
- ip.cn(不支持 cURL)
- ipinfo.io
- cip.cc
- ifconfig.me
- myip.ipip.net
样例
ip-api.com
1 | curl 'http://ip-api.com/json/?lang=zh-CN' |
返回结果:
1 | { |
ipecho.net
1 | curl ipecho.net/plain |
返回结果:
1 | 168.63.213.70 |
ipinfo.io
1 | curl ipinfo.io |
返回结果:
1 | { |
cip.cc
1 | curl cip.cc |
返回结果:
1 | IP : 111.30.233.219 |
myip.ipip.net
1 | curl myip.ipip.net |
返回结果:
1 | 当前 IP:111.30.233.219 来自于:中国 天津 天津 移动 |
ifconfig.me
1 | curl ifconfig.me |
1 | 111.30.233.219 |
members.3322.org/dyndns/getip
1 | curl members.3322.org/dyndns/getip |
1 | 111.30.233.219 |
作者:舌尖上的大胖
链接:https://www.jianshu.com/p/09363560a833
GitHub Proxy
https://git.951959483.xyz/
终端命令行
支持终端命令行 git clone、wget、curl 等工具下载。支持 raw.githubusercontent.com、gist.github.com、gist.githubusercontent.com 文件下载。
**注意:**不支持 SSH Key 方式 git clone 下载。
git clone
1 | git clone https://git.951959483.xyz/https://github.com/stilleshan/ServerStatus |
git clone 私有仓库
Clone 私有仓库需要在 Personal access tokens 申请 Token 配合使用:
1 | git clone https://user:your_token@git.951959483.xyz/https://github.com/your_name/your_private_repo |
wget & curl
1 | wget https://git.951959483.xyz/https://github.com/stilleshan/ServerStatus/archive/master.zip |
首页下载
在本页地址栏输入合规链接(参考以下链接)点击下载按钮,支持 raw.githubusercontent.com、gist.github.com、gist.githubusercontent.com 文件下载。
Raw 文件
1 | https://raw.githubusercontent.com/stilleshan/ServerStatus/master/Dockerfile |
分支源码
1 | https://github.com/stilleshan/ServerStatus/archive/master.zip |
Releases 源码
1 | https://github.com/stilleshan/ServerStatus/archive/v1.0.tar.gz |
Releases 文件
1 | https://github.com/fatedier/frp/releases/download/v0.33.0/frp_0.33.0_linux_amd64.tar.gz |
githubusercontent、github加速镜像
加速地址一览
- fastgit.org:https://doc.fastgit.org/
- cnpmjs.org:https://github.com.cnpmjs.org/
- gitclone.com:https://gitclone.com/
- gitee:https://gitee.com/mirrors
- GitHub 文件加速:https://gh.api.99988866.xyz/
- Github 仓库加速:https://github.zhlh6.cn/
- Github 仓库加速:http://toolwa.com/github/
加速 clone
1 | # 方法一:手动替换地址 |
加速 release
1 | # 原地址 |
加速 raw
1 | # 原地址 |
Fedora/CentOS下命令行配置Shadowsocks全局代理
输入以下内容,创建 Shadowsocks 配置文件 /etc/shadowsocks.json:
1 | { |
使用以下命令启动服务:
1 | sudo sslocal -c /etc/shadowsocks.json & |
下面开始配置 privoxy 做全局代理:
1 | sudo vi /etc/privoxy/config |
找到并修改以下配置:
1 | listen-address 127.0.0.1:8118 |
去掉注释,保证端口 8118 不与系统变量冲突即可,可自由设定。
找到并修改:
1 | forward-socks5t / 127.0.0.1:1080 . |
去掉注释,要求和 ss 端口号相同,注意最后一位英文句号不可丢!
保存并退出即可。
执行:
1 | sudo privoxy /etc/privoxy/config |
无报错则正确启动。
Shell 下使用 http 代理需执行:
1 | export http_proxy=http://127.0.0.1:8118 |
运行 w3m www.google.com 可访问则说明代理已配置成功。
Fedora & RHEL
Supported distributions:
- Recent Fedora versions (until EOL)
- RHEL 6, 7 and derivatives (including CentOS, Scientific Linux)
Build from source with CentOS
If you are using CentOS 7, you need to install these prerequirements to build from source code:
1 | yum install epel-release -y |
ArchLinux / Manjaro
1 | bash <(curl -sL https://raw.githubusercontent.com/hijkpw/scripts/master/centos_install_ss.sh) |
OpenVZ 平台 Google BBR 一键安装脚本
更新了 liblkl-hijack.so 并打上了最近网上很火的“魔改版” BBR 补丁,同时更新了 haproxy。老版本的朋友可以重新下载安装脚本再安装一遍,需要先停止当前的服务。
使用方法
已测试通过的系统: Ubuntu 14.04 x64、Ubuntu 16.04 x64、CentOS 6 x64、CentOS 7 x64 只支持 64 位系统,要求 glibc 版本 2.14 以上。
| 1 2 3 | wget https://raw.githubusercontent.com/kuoruan/shell-scripts/master/ovz-bbr/ovz-bbr-installer.sh chmod +x ovz-bbr-installer.sh ./ovz-bbr-installer.sh |
|---|
需要配置的有如下几个选项:
1.需要加速的端口,即的 SS 端口。加速开启之后,流量会先经过 BBR 处理,之后再发送给后端的 SS。
2.可能需要配置 “公网接口名称”,即你服务器上具有公网 IP 的接口名称。搬瓦工 OpenVZ 上默认都是 venet0,但是有朋友可能需要安装在其他服务器上,所以我加入了此选项。
需要注意的是,在有 firewalld 的服务器上安装的时候,firewalld 会干扰 iptables 的规则,造成网络不通(现在具体原因未知,谁有解决方案可以提示一下)。所以在装有 firewalld 的服务器上需要先退出 firewalld:
| 1 2 | systemctl disable firewalld systemctl stop firewalld |
|---|
如需卸载,请使用:
| 1 | ./ovz-bbr-installer.sh uninstall |
|---|
错误说明
有些机器一切正常,但是加速失败。从网友的反馈来看,可能需要将 SS 的监听地址从 vps IP 改到 127.0.0.1 或者 0.0.0.0,具体未测试,加速失败的朋友可以试一试
多端口加速
安装的时候只配置了一个加速端口,但是你可以配置多端口加速,配置方法非常简单。 修改文件
| 1 | # vi /usr/local/haproxy-lkl/etc/port-rules |
|---|
在文件里添加需要加速的端口,每行一条,可以配置单个端口或者端口范围,以 # 开头的行将被忽略。 例如:8800 或者 8800-8810 配置完成之后,只需要重启 haproxy-lkl 即可。
注: 最初版本的实现是需要再开一个新端口,后来经人提醒,我又看了一下 HAproxy 的配置说明,可以直接代理后端端口,不必再开新端口。请注意,使用该方法后,如果 HAproxy 进程异常退出,会造成无法连接原有端口。所以,请确保在退出 HAproxy 时是通过命令正常退出的,在退出时会自动清理原有的防火墙规则。
使用 systemctl 或者 service 命令来启动、停止和重启 HAporxy-lkl:
| 1 | systemctl {start|stop|restart} haproxy-lkl |
|---|
| 1 | service haproxy-lkl {start|stop|restart} |
|---|
/usr/local/haproxy-lkl/etc/haproxy.cfg 这个文件是通过 port-rules 自动生成的,每次启动都会重新生成,所以直接修改它的配置没用。 如果想要自定义配置,请修改启动文件:
| 1 | /usr/local/haproxy-lkl/sbin/haproxy-lkl |
|---|
更新 glibc
CentOS 6 更新 glibc,首先下载如下几个文件:
然后安装:
| 1 2 3 4 5 | # rpm -Uvh glibc-2.15-60.el6.x86_64.rpm \ glibc-common-2.15-60.el6.x86_64.rpm \ glibc-devel-2.15-60.el6.x86_64.rpm \ glibc-headers-2.15-60.el6.x86_64.rpm \ nscd-2.15-60.el6.x86_64.rpm |
|---|
如果以上步骤无法更新,可以手动编译更新(来自网友的方法)
| 1 2 3 4 5 6 7 8 9 | wget http://ftp.gnu.org/gnu/glibc/glibc-2.15.tar.gz wget http://ftp.gnu.org/gnu/glibc/glibc-ports-2.15.tar.gz tar -zxf glibc-2.15.tar.gz tar -zxf glibc-ports-2.15.tar.gz mv glibc-ports-2.15 glibc-2.15/ports mkdir glibc-build-2.15 cd glibc-build-2.15 ../glibc-2.15/configure --prefix=/usr --disable-profile --enable-add-ons --with-headers=/usr/include --with-binutils=/usr/bin make all && make install |
|---|
检查一下:
| 1 2 3 4 5 6 | # ldd –version ldd (GNU libc) 2.15 Copyright (C) 2012 Free Software Foundation, Inc. This is free software; see the source for copying conditions. There is NO warranty; not even for MERCHANTABILITY or FITNESS FOR A PARTICULAR PURPOSE. Written by Roland McGrath and Ulrich Drepper. |
|---|
已经升级到 glibc 2.15 了。
判断 BBR 已正常工作
判断 bbr 是否正常启动可以尝试 ping 10.0.0.2,如果能通,说明 bbr 已经启动。
然后检查 iptables 规则
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 | iptables -t nat -nL Chain PREROUTING (policy ACCEPT) target prot opt source destination LKL_IN all -- 0.0.0.0/0 0.0.0.0/0 Chain POSTROUTING (policy ACCEPT) target prot opt source destination Chain OUTPUT (policy ACCEPT) target prot opt source destination Chain LKL_IN (1 references) target prot opt source destination DNAT tcp -- 0.0.0.0/0 0.0.0.0/0 tcp dpt:8989 to:10.0.0.2 |
|---|
里边会看到多了一张链表 LKL_IN,里边有相应的端口规则。
内核开启BBR方法
1. 修改系统变量
1 | sudo su |
2. 保存生效
1 | sysctl -p |
3. 查看内核是否已开启 BBR
1 | sysctl net.ipv4.tcp_available_congestion_control |
显示以下即已开启:
1 | # sysctl net.ipv4.tcp_available_congestion_control |
4. 查看 BBR 是否启动
1 | lsmod | grep bbr |
显示以下即启动成功:
1 | # lsmod | grep bbr |
Linux下firewallD简单上手
| 导读 | FirewallD 是 CentOS 7 服务器上默认可用的防火墙管理工具。基本上,它是 iptables 的封装,有图形配置工具 firewall-config 和命令行工具 firewall-cmd。使用 iptables 服务,每次改动都要求刷新旧规则,并且从 /etc/sysconfig/iptables 读取新规则,然而 firewalld 只应用改动了的不同部分。 |
|---|
FirewallD 使用服务(service) 和区域(zone)来代替 iptables 的规则(rule)和链(chain)。
默认情况下,有以下的区域(zone)可用:
- drop – 丢弃所有传入的网络数据包并且无回应,只有传出网络连接可用。
- block — 拒绝所有传入网络数据包并回应一条主机禁止的 ICMP 消息,只有传出网络连接可用。
- public — 只接受被选择的传入网络连接,用于公共区域。
- external — 用于启用了地址伪装的外部网络,只接受选定的传入网络连接。
- dmz — DMZ 隔离区,外部受限地访问内部网络,只接受选定的传入网络连接。
- work — 对于处在你工作区域内的计算机,只接受被选择的传入网络连接。
- home — 对于处在你家庭区域内的计算机,只接受被选择的传入网络连接。
- internal — 对于处在你内部网络的计算机,只接受被选择的传入网络连接。
- trusted — 所有网络连接都接受。
要列出所有可用的区域,运行:
1 | firewall-cmd --get-zones |
列出默认的区域:
1 | firewall-cmd --get-default-zone |
改变默认的区域:
1 | firewall-cmd --set-default-zone=dmz |
FirewallD 服务
FirewallD 服务使用 XML 配置文件,记录了 firewalld 服务信息。
列出所有可用的服务:
1 | firewall-cmd --get-services |
XML 配置文件存储在 /usr/lib/firewalld/services/ 和 /etc/firewalld/services/ 目录下。
用 FirewallD 配置防火墙
作为一个例子,假设你正在运行一个 web 服务器,SSH 服务端口为 7022,以及邮件服务,你可以利用 FirewallD 这样配置你的服务器:
首先设置默认区为 dmz:
1 | firewall-cmd --set-default-zone=dmz |
为 dmz 区添加持久性的 HTTP 和 HTTPS 规则:
1 | firewall-cmd --zone=dmz --add-service=http --permanent |
开启端口 25 (SMTP) 和端口 465 (SMTPS):
1 | firewall-cmd --zone=dmz --add-service=smtp --permanent |
开启 IMAP、IMAPS、POP3 和 POP3S 端口:
1 | firewall-cmd --zone=dmz --add-service=imap --permanent |
因为将 SSH 端口改到了 7022,所以要移除 ssh 服务(端口 22),开启端口 7022:
1 | firewall-cmd --remove-service=ssh --permanent |
要应用这些更改,我们需要重新加载防火墙:
1 | firewall-cmd --reload |
最后可以列出这些规则:
1 | firewall-cmd --list-all |
via: Set Up and Configure a Firewall with FirewallD on CentOS 7
译者简介:
Locez 是一个喜欢技术,喜欢折腾的 Linuxer,靠着对 Linux 的兴趣自学了很多 Linux 相关的知识,并且志在于为 Linux 在中国普及出一份力。
作者:rosehosting.com 译者:Locez 校对:jasminepeng
Allow ssh port on SELinux
Step 3: Allow new SSH port on SELinux
The default port labelled for SSH is 22.
1 | semanage port -l | grep ssh |
输出:
1 | ssh_port_t tcp 22 |
If you want to allow sshd to bind to network port configured, then you need to modify the port type to ssh_port_t.
1 | sudo semanage port -a -t ssh_port_t -p tcp 2200 |
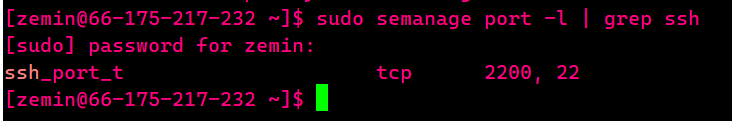
Confirm that the new port has been added to list of allowed ports for ssh:
1 | semanage port -l | grep ssh |
输出:
1 | ssh_port_t tcp 2200, 22 |
Step 4: Open SSH port on Firewalld
It is always recommended to keep the Firewall service running and only allow trusted services.
1 | sudo firewall-cmd --add-port=2200/tcp --permanent |
设置 SSH 通过密钥登录
我们一般使用 PuTTY 等 SSH 客户端来远程管理 Linux 服务器。但是,一般的密码方式登录,容易有密码被暴力破解的问题。所以,一般我们会将 SSH 的端口设置为默认的 22 以外的端口,或者禁用 root 账户登录。其实,有一个更好的办法来保证安全,而且让你可以放心地用 root 账户从远程登录——那就是通过密钥方式登录。
密钥形式登录的原理是:利用密钥生成器制作一对密钥——一只公钥和一只私钥。将公钥添加到服务器的某个账户上,然后在客户端利用私钥即可完成认证并登录。这样一来,没有私钥,任何人都无法通过 SSH 暴力破解你的密码来远程登录到系统。此外,如果将公钥复制到其他账户甚至主机,利用私钥也可以登录。
下面来讲解如何在 Linux 服务器上制作密钥对,将公钥添加给账户,设置 SSH,最后通过客户端登录。
1. 制作密钥对
首先在服务器上制作密钥对。首先用密码登录到你打算使用密钥登录的账户,然后执行以下命令:
1 | ssh-keygen <== 建立密钥对 |
运行输出示例:
1 | Generating public/private rsa key pair. |
密钥锁码在使用私钥时必须输入,这样就可以保护私钥不被盗用。当然,也可以留空,实现无密码登录。
现在,在 root 用户的家目录中生成了一个 .ssh 的隐藏目录,内含两个密钥文件。id_rsa 为私钥,id_rsa.pub 为公钥。
2. 在服务器上安装公钥
键入以下命令,在服务器上安装公钥:
1 | cd .ssh |
如此便完成了公钥的安装。为了确保连接成功,请保证以下文件权限正确:
1 | chmod 600 authorized_keys |
3. 设置 SSH,打开密钥登录功能
编辑 /etc/ssh/sshd_config 文件,进行如下设置:
1 | RSAAuthentication yes |
另外,请留意 root 用户能否通过 SSH 登录:
1 | PermitRootLogin yes |
当你完成全部设置,并以密钥方式登录成功后,再禁用密码登录:
1 | PasswordAuthentication no |
最后,重启 SSH 服务:
1 | sudo systemctl restart sshd |